
Linux
OpenAI Found 948 Linux Kernel Bugs. That Is Not a 948-Patch Emergency
OpenAI's agent pipeline produced 948 Linux kernel patches, but maintainers still have to review relevance, duplicates, affected versions, and fixes.

WealthLab publishes source-backed, hands-on guides to Docker, Ghost, VPS operations, backups, security, and practical software decisions. The publication runs on a live self-hosted Ghost and Docker stack. Read the About page and editorial methodology.
Linux
OpenAI's agent pipeline produced 948 Linux kernel patches, but maintainers still have to review relevance, duplicates, affected versions, and fixes.

AI Agents
Google plans a microVM service that separates the agent harness from an isolated computer. Here is what is confirmed, what remains open, and who should wait.
Security
CVE-2026-103916 crossed the sandbox boundary through a user-run copy, not a microVM escape. Here is who is affected and why the distinction matters.
Security
OpenAI is expanding model-assisted security work, while the Hugging Face incident shows why authorization and containment must be designed separately.
Security
GitHub's December 2 secure default changes how public repositories run pull_request_target workflows. Learn who is affected and how to preserve safe automation.
AI Agents
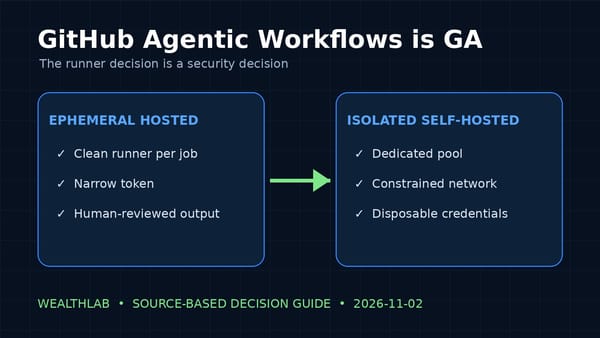
GitHub Agentic Workflows is generally available. This decision guide examines the security boundary, self-hosted runner trade-offs, and safer first use cases.
Docker
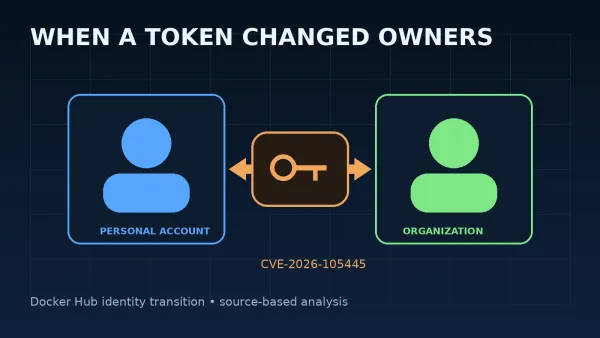
Docker fixed a Hub account-conversion flaw that could silently reassign a live personal access token. Here is what the incident means for registry trust and cleanup.
Docker
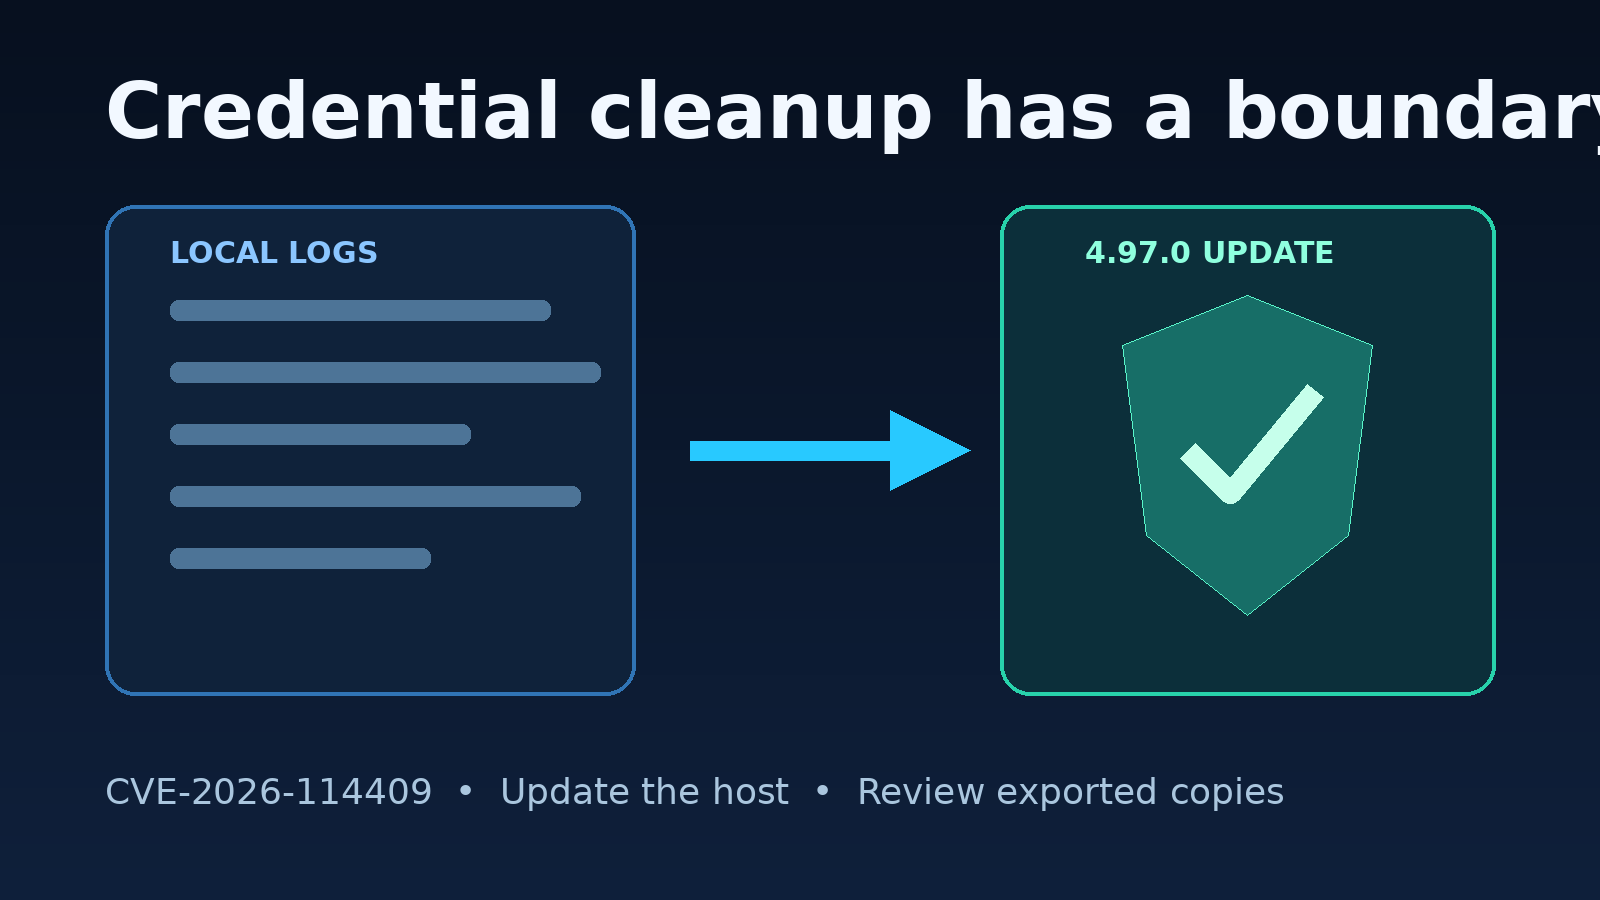
CVE-2026-114409 could expose third-party API keys and OAuth tokens in local logs. Updating cleans host files, but exported copies need separate review.
n8n
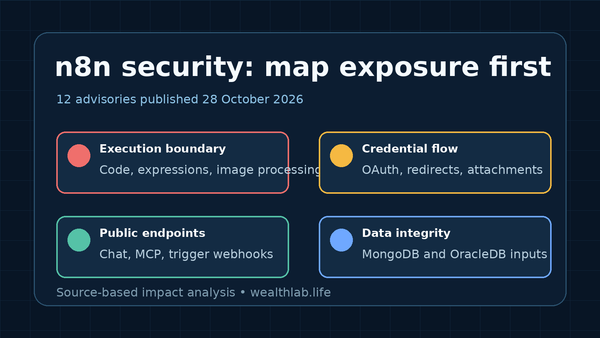
n8n published 12 advisories spanning code execution, credential leakage, public endpoints, and data integrity. Here is how to prioritize exposure.
AI Agents
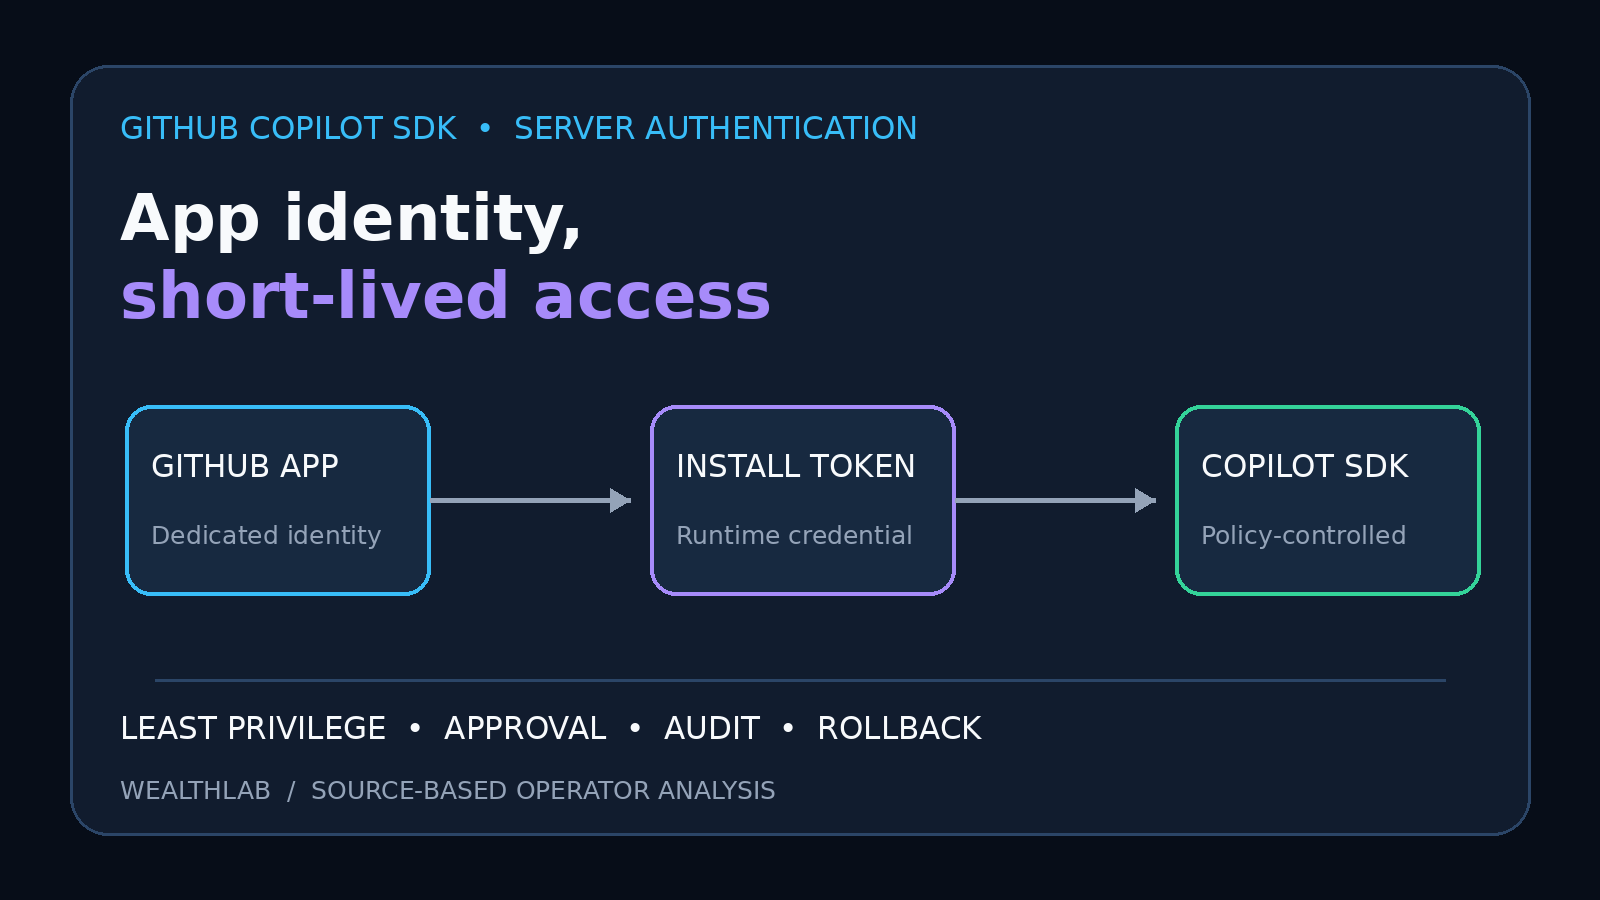
GitHub Apps can now authenticate Copilot SDK services without a user session. Review permissions, token handling, access policy, and rollback first.
AI Agents
Agent Skills now has a vendor-neutral home, but portability is not a security boundary. Use this adoption and review checklist before running a skill.
Security
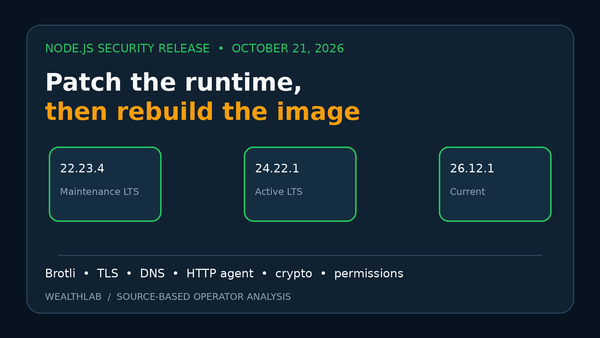
Node.js fixed high-severity Brotli, TLS, and DNS flaws. Container operators should update, rebuild, redeploy, and verify the runtime—not only npm packages.