
OpenAI Found 948 Linux Kernel Bugs. That Is Not a 948-Patch Emergency
OpenAI's agent pipeline produced 948 Linux kernel patches, but maintainers still have to review relevance, duplicates, affected versions, and fixes.

OpenAI's agent pipeline produced 948 Linux kernel patches, but maintainers still have to review relevance, duplicates, affected versions, and fixes.

Google plans a microVM service that separates the agent harness from an isolated computer. Here is what is confirmed, what remains open, and who should wait.
CVE-2026-103916 crossed the sandbox boundary through a user-run copy, not a microVM escape. Here is who is affected and why the distinction matters.
OpenAI is expanding model-assisted security work, while the Hugging Face incident shows why authorization and containment must be designed separately.
GitHub's December 2 secure default changes how public repositories run pull_request_target workflows. Learn who is affected and how to preserve safe automation.
GitHub Agentic Workflows is generally available. This decision guide examines the security boundary, self-hosted runner trade-offs, and safer first use cases.
Docker fixed a Hub account-conversion flaw that could silently reassign a live personal access token. Here is what the incident means for registry trust and cleanup.
CVE-2026-114409 could expose third-party API keys and OAuth tokens in local logs. Updating cleans host files, but exported copies need separate review.
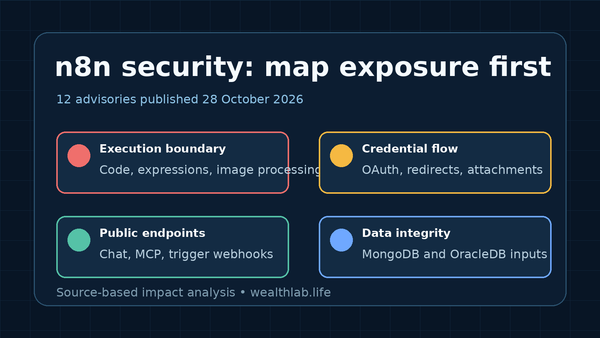
n8n published 12 advisories spanning code execution, credential leakage, public endpoints, and data integrity. Here is how to prioritize exposure.
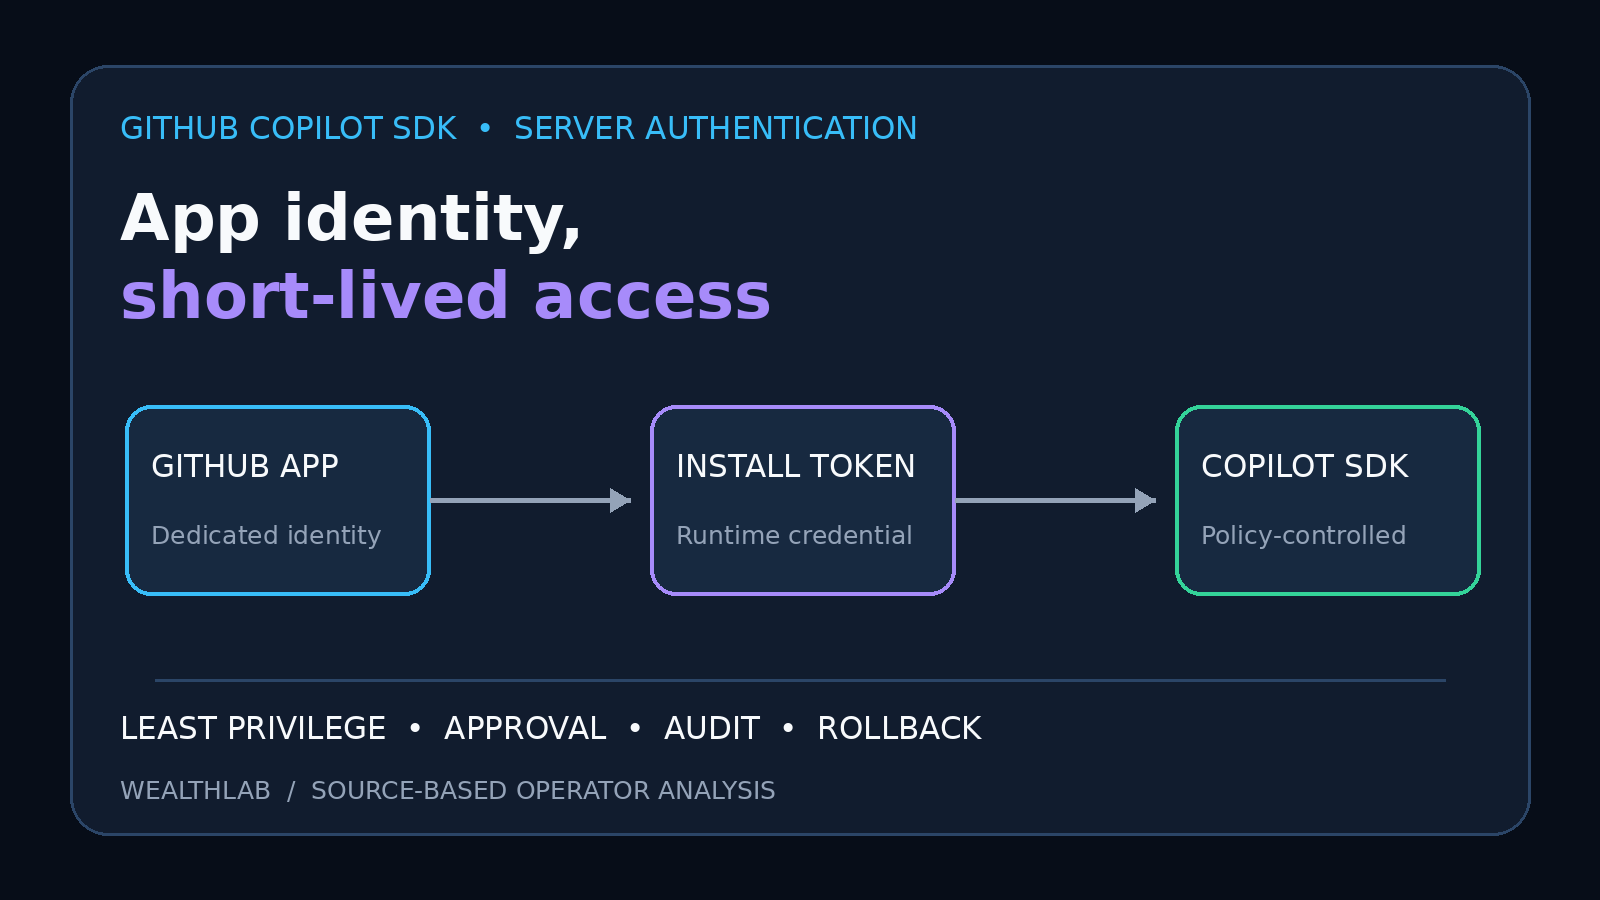
GitHub Apps can now authenticate Copilot SDK services without a user session. Review permissions, token handling, access policy, and rollback first.
Agent Skills now has a vendor-neutral home, but portability is not a security boundary. Use this adoption and review checklist before running a skill.
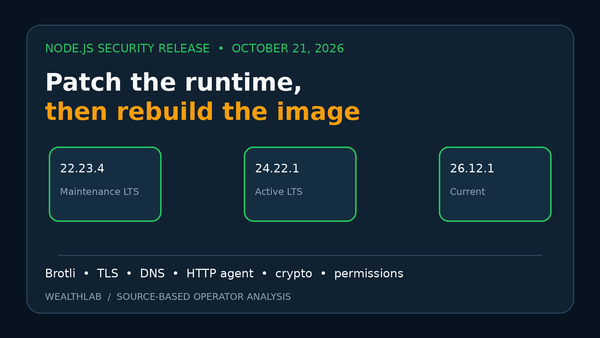
Node.js fixed high-severity Brotli, TLS, and DNS flaws. Container operators should update, rebuild, redeploy, and verify the runtime—not only npm packages.
Docker
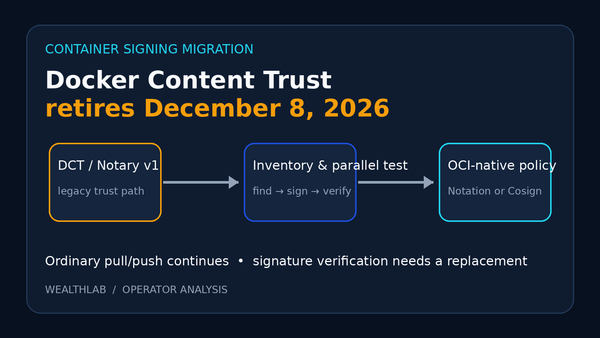
Docker will shut down notary.docker.io on December 8, 2026. Audit DCT dependencies and replace verification before disabling the legacy path.
Security
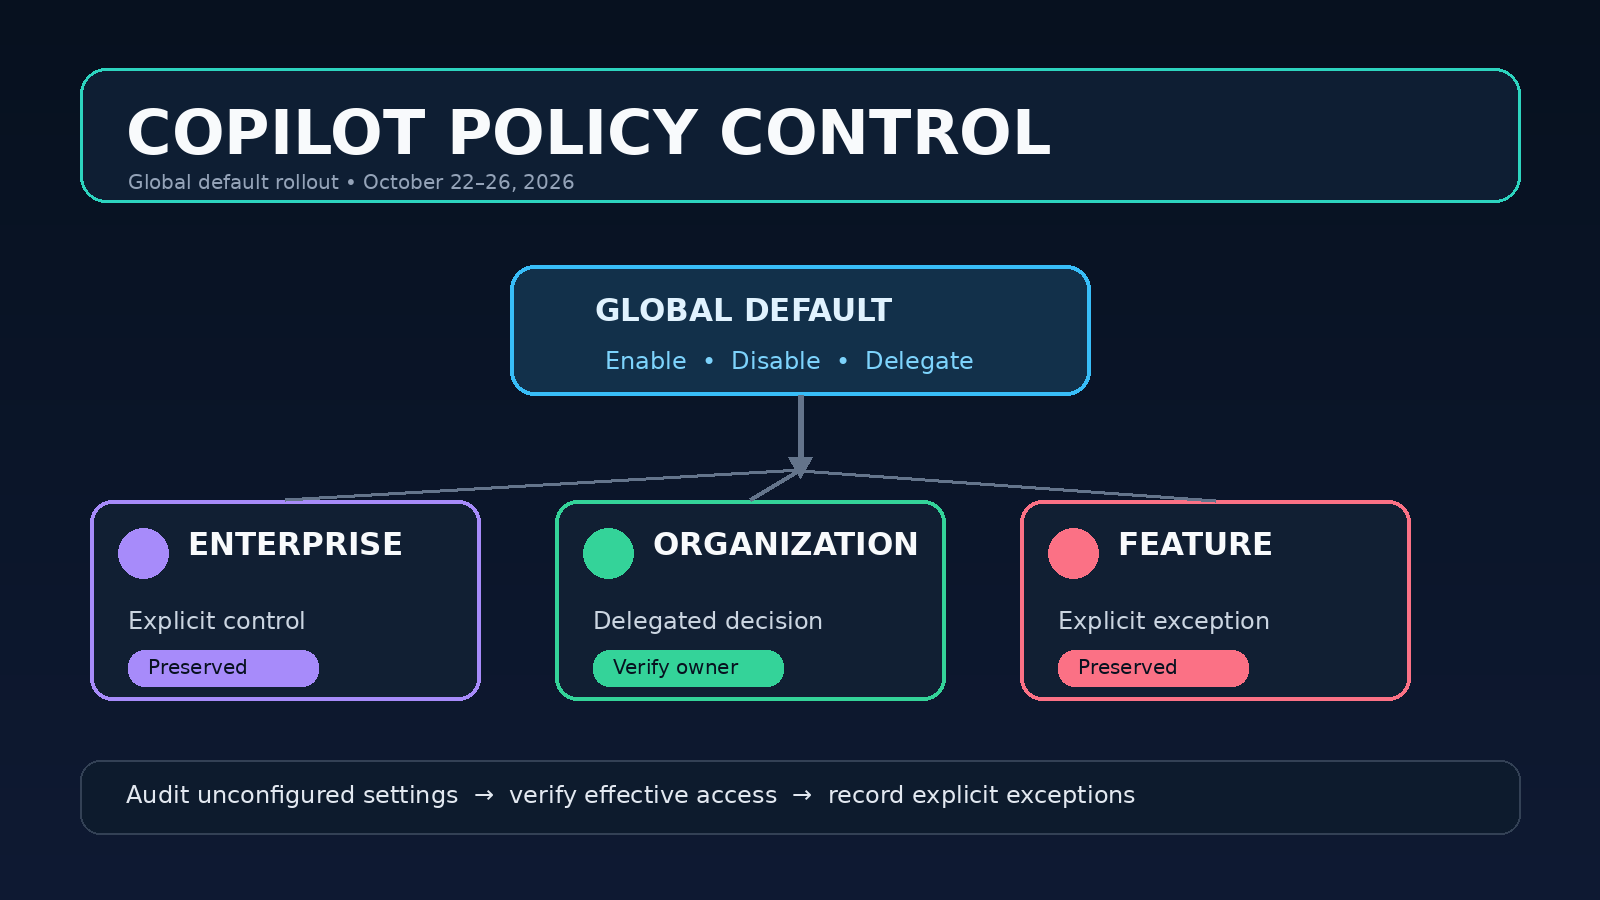
GitHub is applying Copilot's global default to eligible unconfigured features through October 26. Audit policy inheritance before access changes silently.
Security
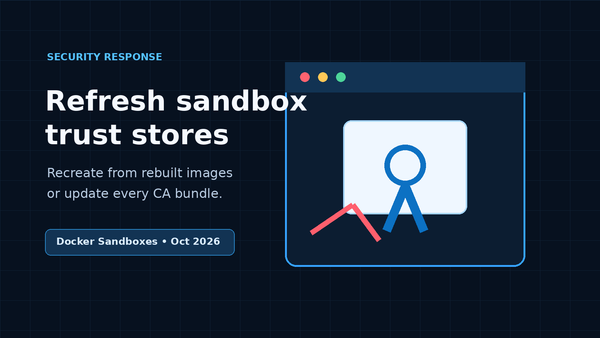
Docker rebuilt its built-in sandbox images after the eMudhra CA compromise. Existing sandboxes need recreation or trust-store updates.
Security
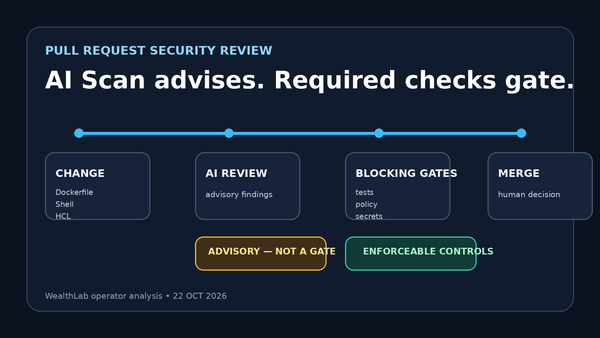
GitHub AI Scan covers pull-request changes beyond CodeQL, but its findings cannot block merges. Use it as review evidence, not a security gate.
AI Agents
GitHub Copilot local sandboxing limits agent access to files and networks, but operators still need to review defaults, credentials, and exceptions.
Security
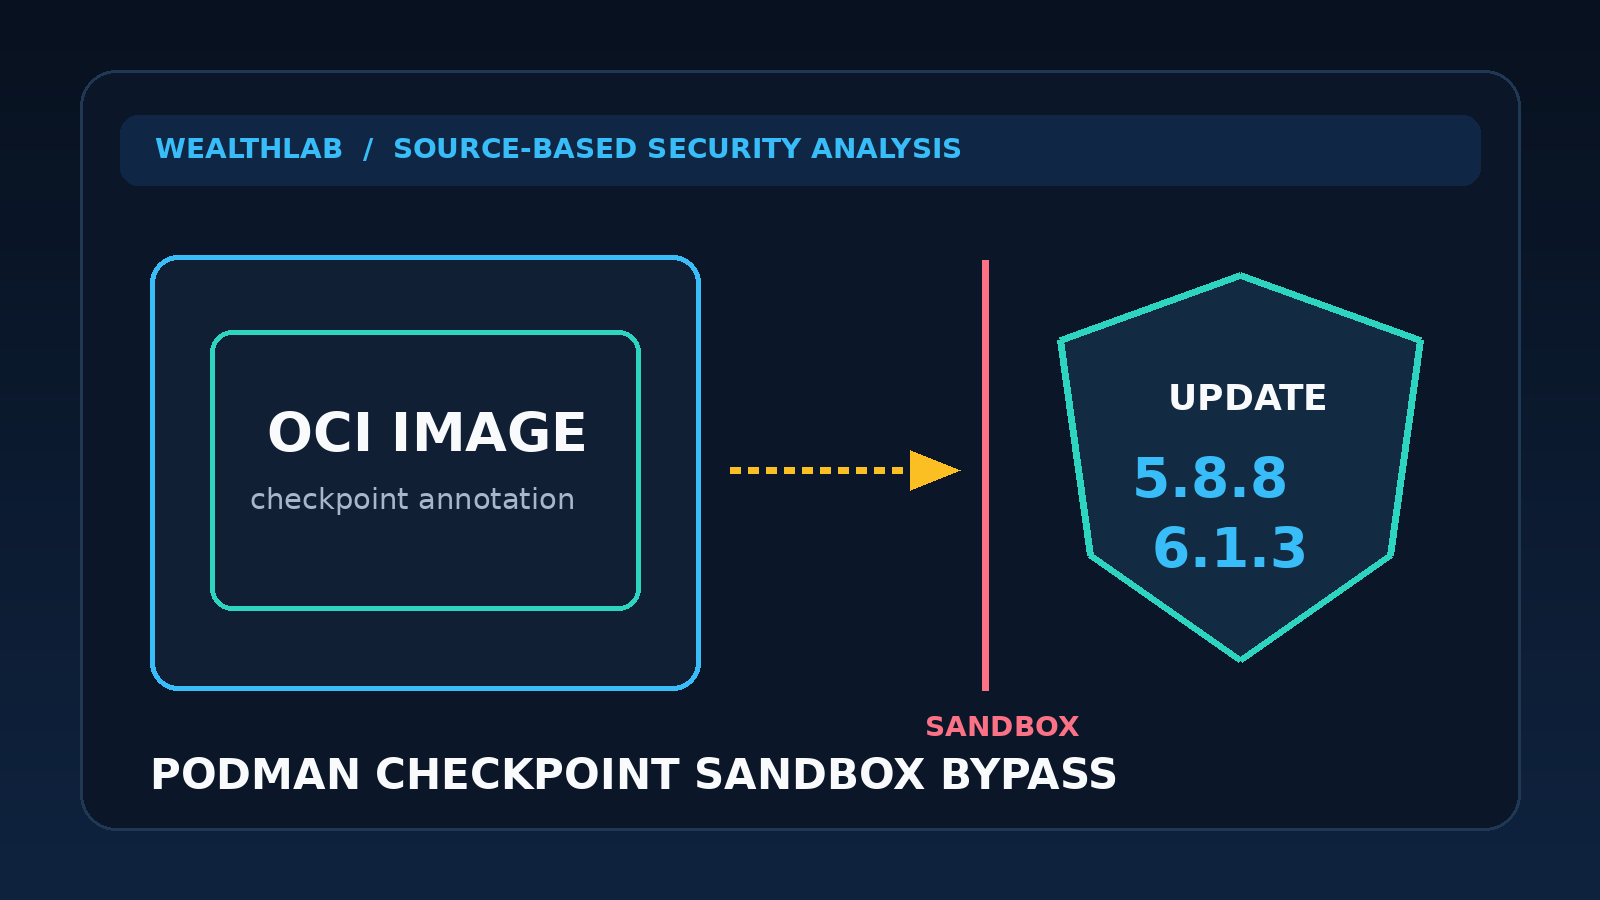
Podman before 5.8.8 or 6.1.3 could let checkpoint metadata override sandbox controls. Check versions, image trust, rootful exposure, and updates.
AI Agents
Claude Code before 2.1.179 could bypass a plugin commit pin. Update, verify versions, review plugin sources, and rotate exposed secrets when warranted.
Docker
Docker Engine 29.9.1 updates containerd for three image-pull flaws involving daemon crashes and host disk exhaustion. Check runtime versions, registry trust, capacity, and rollback readiness.
n8n
n8n disclosed 15 high- and medium-severity issues on October 14. Check your branch, back up state, patch promptly, and review exposed workflows and credentials.
Docker
Docker fixed a critical Hub token-transfer flaw. Check whether you were notified, review PATs and image history, rotate CI credentials, and strengthen registry controls.
n8n
Prepare a self-hosted n8n instance for 3.0: verify the release channel, run the Migration Report, replace removed nodes, back up, stage, and test rollback.
Hermes Agent
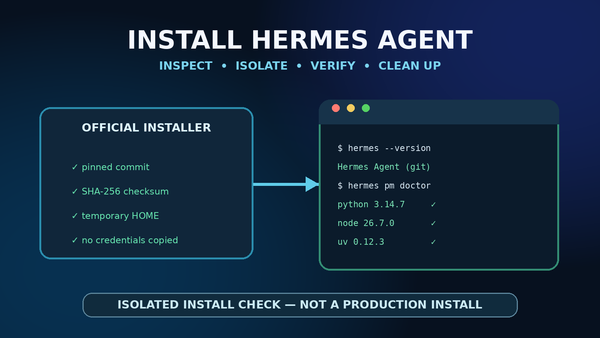
Install Hermes Agent on Linux with an inspect-first workflow, isolated validation, exact observed results, troubleshooting, cleanup, and evidence limits.