
Security
Docker Sandboxes 0.51.0 Closes an sbx cp Path Escape
CVE-2026-103916 crossed the sandbox boundary through a user-run copy, not a microVM escape. Here is who is affected and why the distinction matters.

Security
CVE-2026-103916 crossed the sandbox boundary through a user-run copy, not a microVM escape. Here is who is affected and why the distinction matters.
Docker
Docker fixed a Hub account-conversion flaw that could silently reassign a live personal access token. Here is what the incident means for registry trust and cleanup.
Docker
CVE-2026-114409 could expose third-party API keys and OAuth tokens in local logs. Updating cleans host files, but exported copies need separate review.
Security
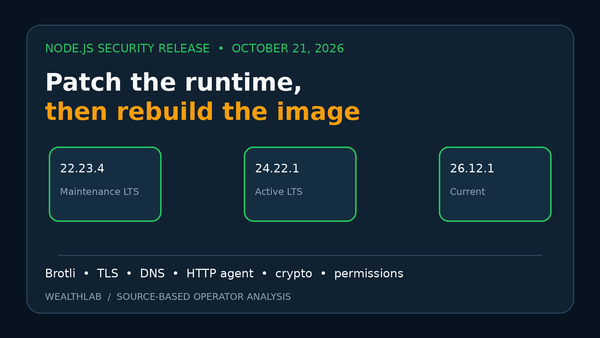
Node.js fixed high-severity Brotli, TLS, and DNS flaws. Container operators should update, rebuild, redeploy, and verify the runtime—not only npm packages.
Docker
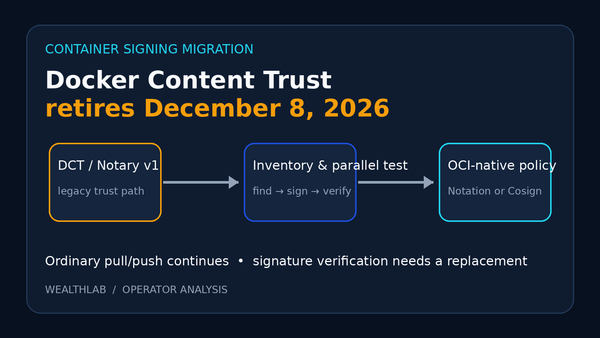
Docker will shut down notary.docker.io on December 8, 2026. Audit DCT dependencies and replace verification before disabling the legacy path.
Security
Docker rebuilt its built-in sandbox images after the eMudhra CA compromise. Existing sandboxes need recreation or trust-store updates.
Docker
Docker Engine 29.9.1 updates containerd for three image-pull flaws involving daemon crashes and host disk exhaustion. Check runtime versions, registry trust, capacity, and rollback readiness.
n8n
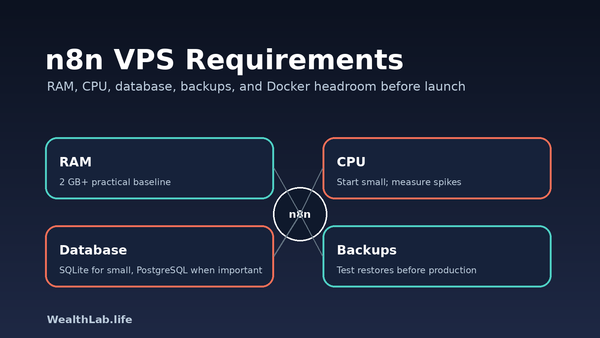
n8n disclosed 15 high- and medium-severity issues on October 14. Check your branch, back up state, patch promptly, and review exposed workflows and credentials.
Docker
Docker fixed a critical Hub token-transfer flaw. Check whether you were notified, review PATs and image history, rotate CI credentials, and strengthen registry controls.
n8n
Prepare a self-hosted n8n instance for 3.0: verify the release channel, run the Migration Report, replace removed nodes, back up, stage, and test rollback.
Vultr
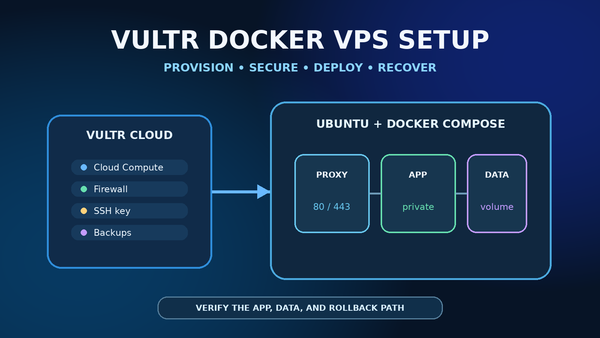
Set up a Vultr Docker VPS with deliberate sizing, SSH, firewall rules, Compose networking, persistent data, backups, and production checks.
Docker
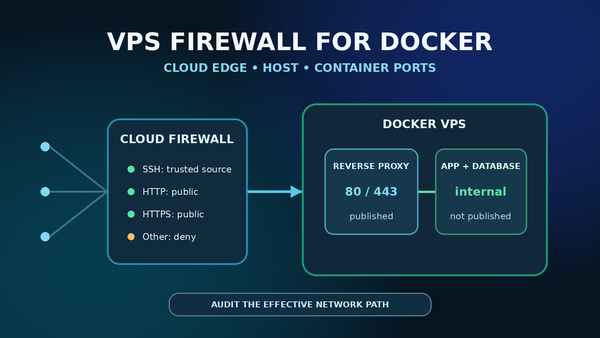
Secure a Docker VPS with provider, host, and Docker-aware firewall controls while keeping databases and admin ports private.